Documentation
Everything you need to get up and running with nPro.
01 Installation
nPro follows the KISS principle. Our installer handles everything from system detection to database configuration with a single command.
curl -sL https://download.npro.ai/download/install.sh | sudo bash Deployment Output Example
[-] System Detected (Ubuntu 24.04)......................... [DONE]
[-] Prerequisites & Repositories........................... [DONE]
[-] nPro Manager Installation/Update...................... [DONE]
[-] Starting nPro Manager Service......................... [DONE]
[-] Verifying API Health................................... [DONE]
[-] ClickHouse Installation................................ [DONE]
[-] Verifying Database Connection (User: admin)............ [DONE]
[-] Npro Backend Installation/Update....................... [DONE]
[-] Starting Backend Service............................... [DONE]
[-] Verifying Backend Health............................... [DONE]
[-] Network Configuration (Ports: 1515, 1514, 21560)....... [DONE]
===========================================================
INSTALLATION/UPDATE COMPLETE
===========================================================
Access: http://192.168.1.1:21560
Credentials: admin / admin
Change the default password first
The installer creates an admin account with the password admin. Log in and change it before you deploy any agents or expose port 21560 beyond your own network.
02 Agent Deployment
Installing the server gets your Host Dashboard running. To actually monitor endpoints, you deploy an nPro agent onto each device. Agents are created and managed from the Agent Dashboard — no manual config files required. Log into your dashboard at http://<your-server-ip>:21560, then open Agents → Deploy New Device to begin.
The Deploy New Device screen walks you through five steps. The installation command in Step 4 is generated automatically from the values you enter in Steps 1–3, so the device name, group, and manager address are already filled in when you copy it.
1 Device Name
Give the device a memorable name so you can identify it later in the dashboard — for example jacks-windows11-laptop. This name is required; it feeds directly into the generated installation script.
2 Select Operating System
Choose the target platform. nPro generates the correct command for each:
- Debian / Ubuntu x64 & ARM
- CentOS / RHEL x64 & ARM
- Apple Silicon (M1/M2/M3) & Intel Mac
- Windows 10 / 11 / Server
3 Assign to Group (optional)
Assign the device to a group (e.g. production, workstations) for cleaner segregation and group-level monitoring policies. You can create a new group inline from this screen. Leave it as default if you don't need grouping yet.
4 Run Installation Script
Copy the generated command and run it on the target device. A Debian/Ubuntu x64 example looks like this (your device name, group, and manager address are filled in automatically):
wget https://packages.npro.ai/agent/npro-agent_amd64.deb && \ sudo NPRO_MANAGER='192.168.1.1' NPRO_AGENT_NAME='jacks-ubuntu-server' \ NPRO_AGENT_GROUP='production' dpkg -i npro-agent_amd64.deb Windows uses a PowerShell Invoke-WebRequest + msiexec command; macOS uses a curl + installer command. The dashboard generates the right one for your selected OS.
5 Start Service Command
Once installed, start the agent service so it connects to your manager. On Linux:
sudo systemctl daemon-reload && sudo systemctl enable npro-agent && sudo systemctl start npro-agent Within about 30 seconds the device appears in your Agent Dashboard and begins streaming events. Windows and macOS start commands are shown on their respective OS selections.
Repeat for each device you want to monitor. The agent communicates outbound to your manager on ports 1514/tcp (events) and 1515/tcp (enrollment) — no inbound ports are required on the endpoint.
03 System Requirements
Network Configuration
Ensure the following ports are open for proper communication:
- 1515/tcp: Agent
- 1514/tcp: Events
- 21560/tcp: UI
Logs & Debugging
You can find critical logs at the following locations:
- /var/log/npro_manager_install.log
- /var/log/clickhouse_install.log
- /var/log/npro_backend_install.log
04 Tech Stack
05 SIEM Features
Unified XDR and SIEM Protection
Combines extended detection and response with security information and event management for comprehensive threat detection, incident response, and compliance.
File Integrity Monitoring (FIM)
Monitors file systems for changes in content, permissions, ownership, and attributes, identifying who made changes and when.
Vulnerability Detection
Collects software inventory and correlates it with CVE databases to identify and alert on vulnerable software for timely remediation.
Active & Incident Response
Automatically triggers countermeasures like blocking connections, stopping processes, or deleting files upon threat detection.
⚡ Offense Monitoring
Offense Monitoring is nPro's risk-based alerting layer. Rather than requiring analysts to triage thousands of individual alerts, the correlation engine groups related security events from the same agent into a single Offense — scored, MITRE-tagged, and ready for investigation.
Accessing Offense Monitoring
Navigate to Offense Monitoring in the left sidebar. The page loads all active offenses ranked by risk score. Offenses with a CRITICAL or HIGH score should be the first stop for any SOC analyst starting a shift.
Reading the Offense Table
| Column | What it means |
|---|---|
| Risk Score | 0–100 composite score. Critical ≥ 85, High ≥ 65, Medium ≥ 40. |
| Agent | Agent ID and device hostname of the affected endpoint. |
| MITRE Tactics | ATT&CK tactics observed in the correlated event cluster (e.g. Defense Evasion, Persistence). |
| Events (24h) | Raw alert count feeding this offense in the past 24 hours. High count = sustained activity. |
| Status | Open / Investigating / Closed / False Positive. |
| Age | Time since last event. Hover for absolute timestamp. |
Triaging an Offense
- 1
Click the offense row
The Offense Details panel slides in from the right, showing agent info, MITRE tactics, source/destination IPs, threat intel status, and the full offense time window (First Seen → Last Seen).
- 2
Mark Investigating
Claim ownership of the offense. This signals to other SOC members that this threat is being actively worked.
- 3
Add Analyst Notes
Document findings at the offense level. Notes persist and are visible to any analyst who opens the offense. Use this for shift handover context.
- 4
Close the offense
Mark as Resolved once remediated, or False Positive if the correlation fired incorrectly. Closed offenses are excluded from the active view.
Tip: Threat Intel IOC match
If an offense shows a red Threat Intel IOC match banner, the agent has matched an indicator from your configured STIX/TAXII feed. Treat these as highest priority regardless of the numeric risk score.
06 NRTG Monitoring
Maps & Dashboards
Visualize your network with real-time data for insights into IT infrastructure health.
Distributed Monitoring
Monitor an unlimited number of remote locations in a single pane of glass.
Alerts & Notifications
Set custom thresholds and receive alerts via email, push, or HTTP requests.
Flexible Probes
Secure communication between all components using TLS encryption.
07 Data Loss Prevention
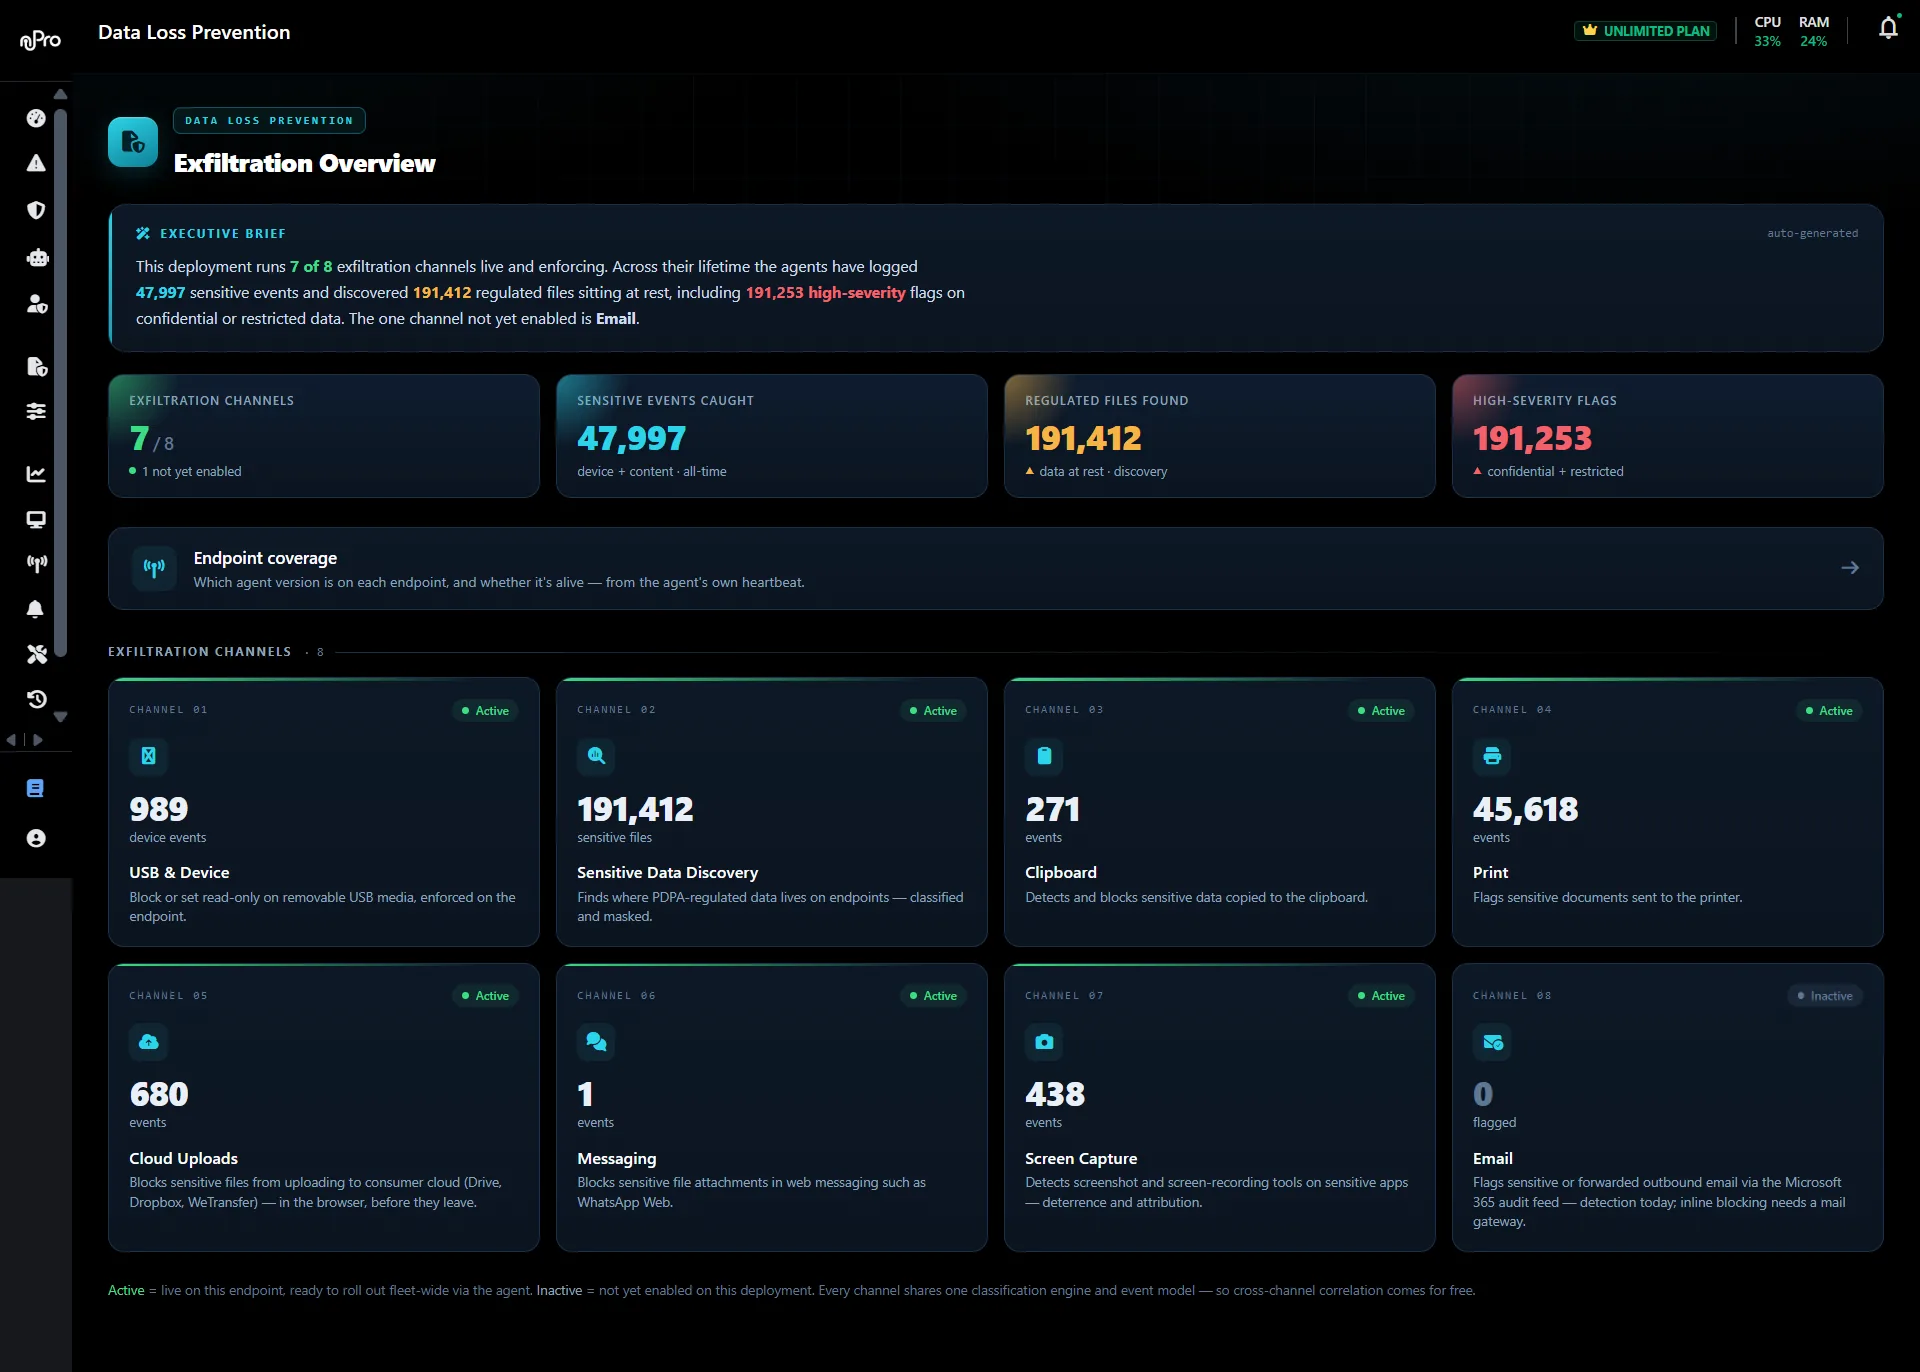
DLP watches eight exfiltration channels from the same agent that runs XDR and SIEM. Every channel shares one classification engine and one event model, so a clipboard event and a USB write correlate without extra configuration. Capability detail is on the DLP page.
Rolling out DLP
- 1
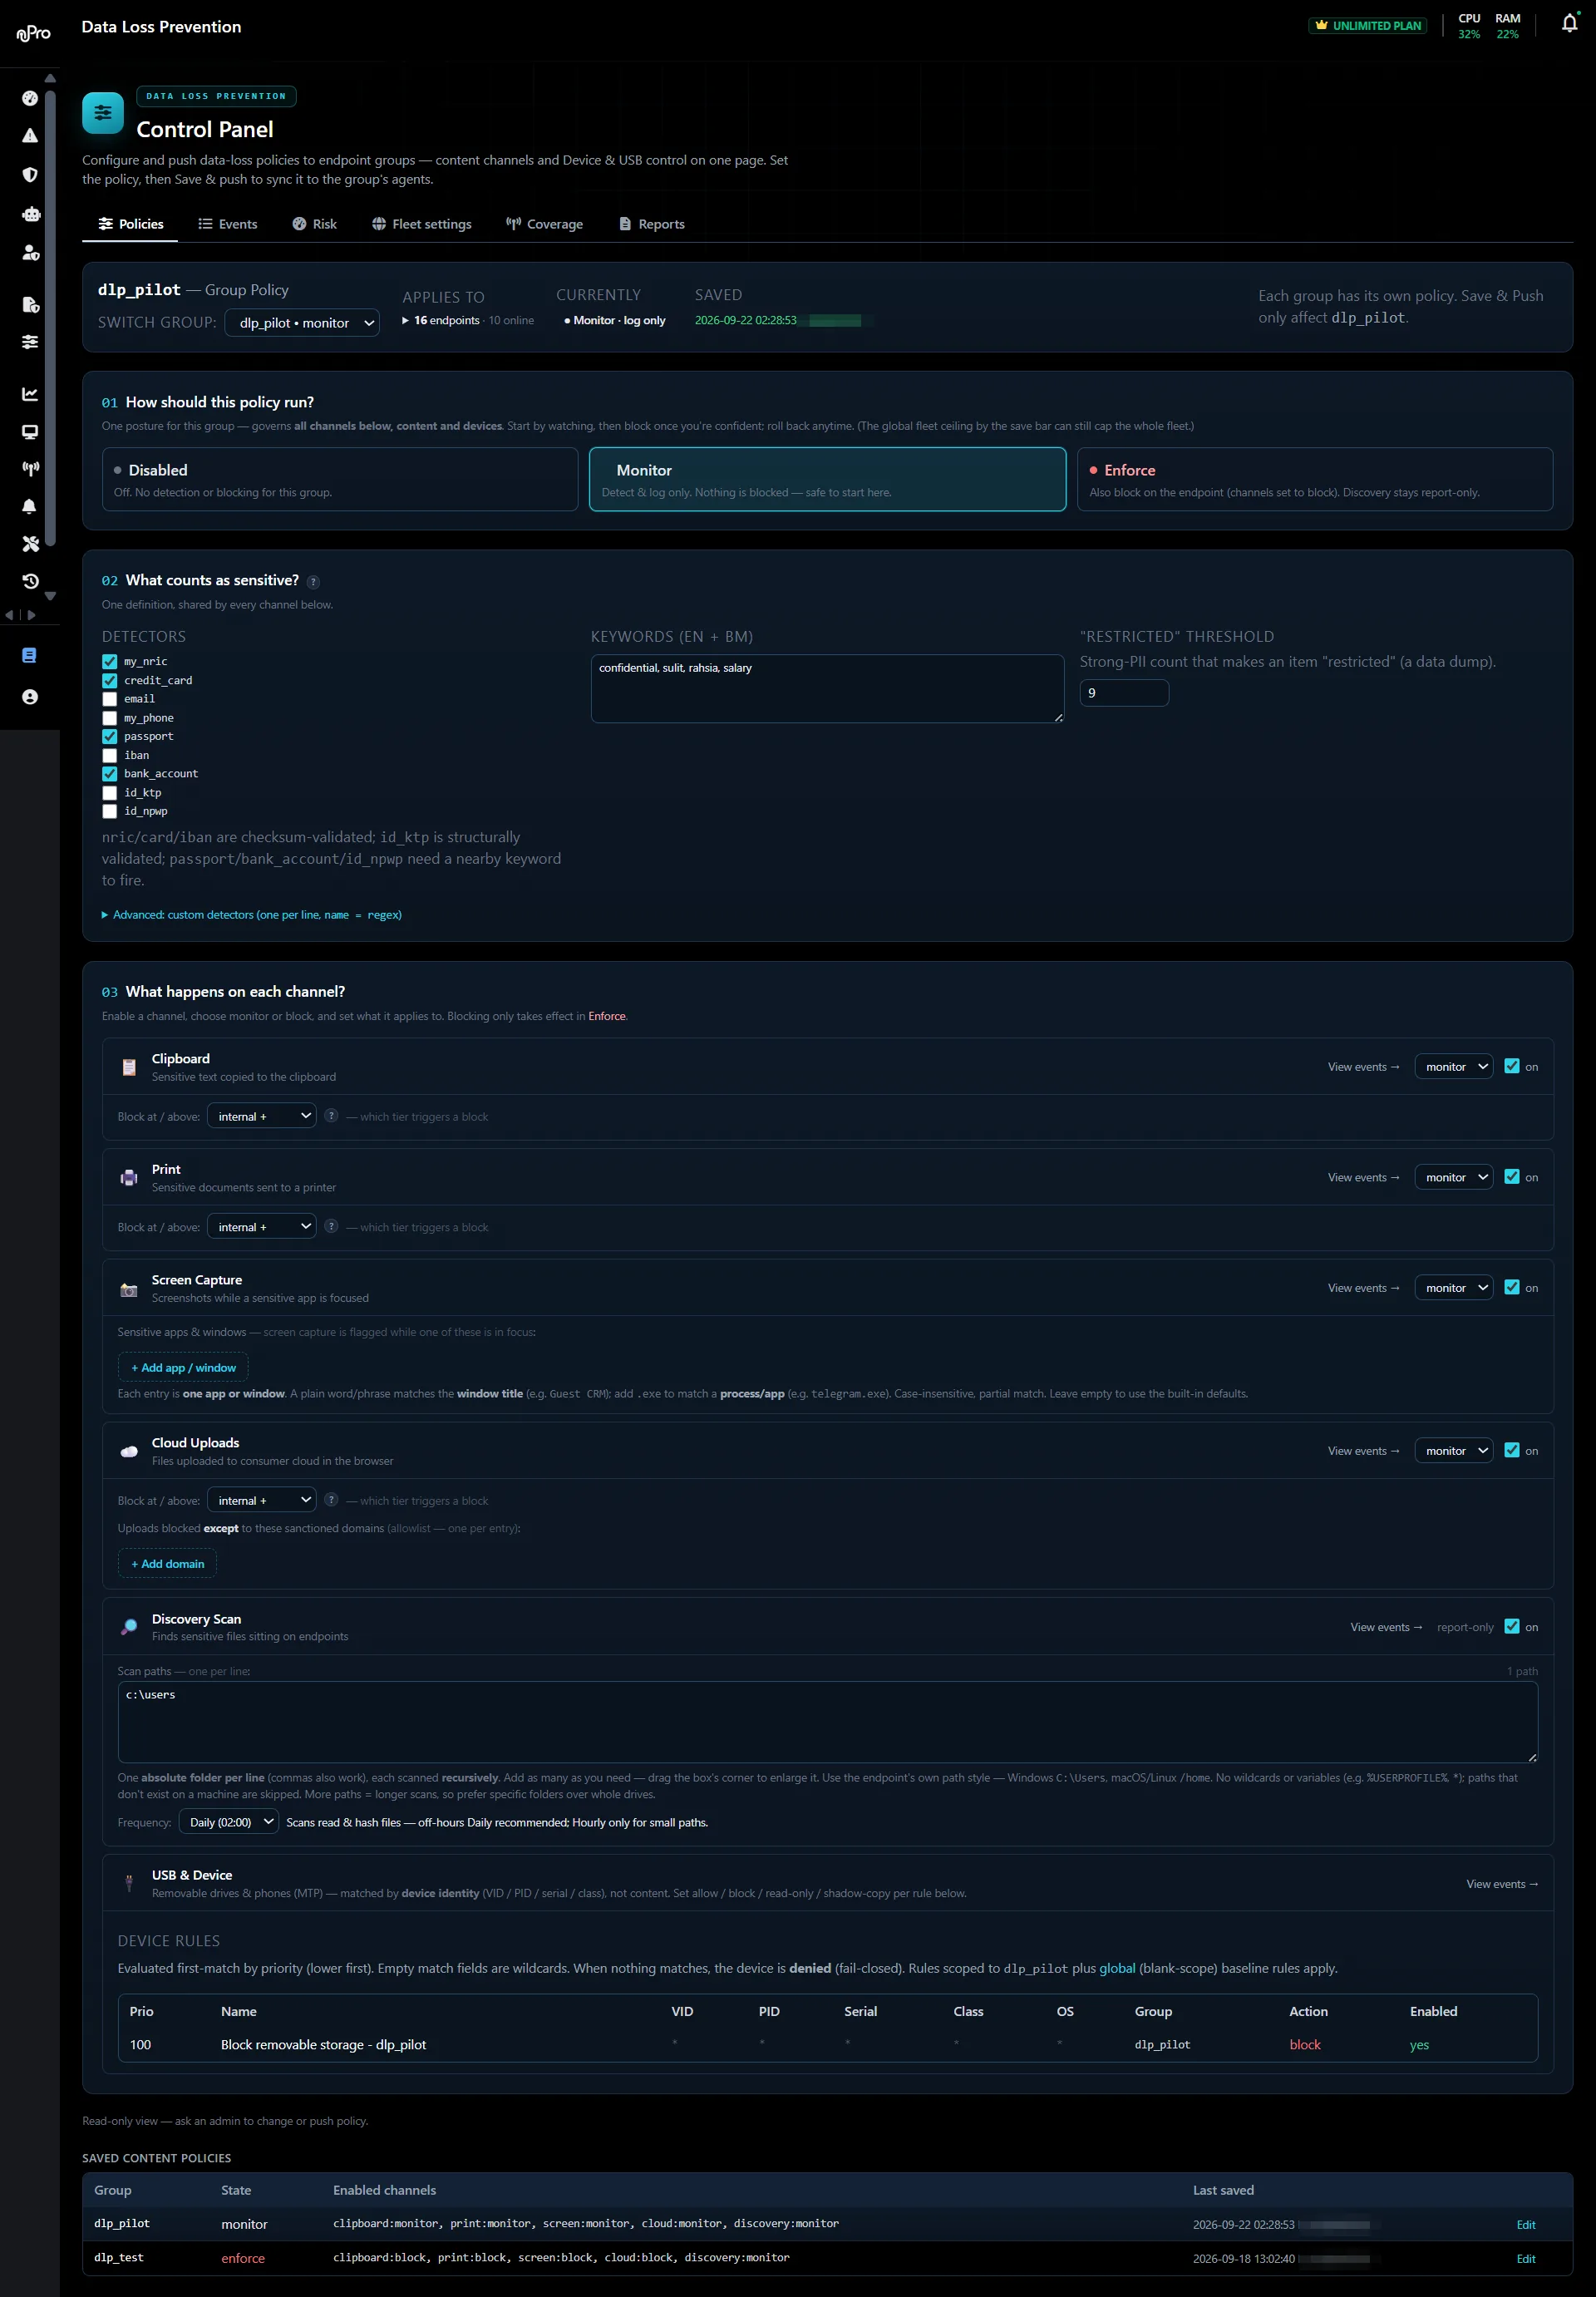
Start every group in Monitor
Monitor detects and logs without stopping anything, so there is no risk to day-to-day work while you learn what normally leaves each group.
- 2
Tune detectors and keywords
Review the events on the Exfiltration Overview, then adjust the detector set and keywords in the Control Panel until what gets flagged matches what you actually care about.
- 3
Move one group to Enforce
Groups move independently, so a high-risk team such as finance can enforce while the rest of the fleet keeps watching. Moving a group into Enforce asks you to type a confirmation phrase, so no one switches a fleet to blocking by accident.
Email is detection only
Outbound email is flagged through your mail platform’s audit feed, so you can see what left, but inline blocking needs a mail gateway and is the next phase rather than something the engine does today.
08 Advanced Integrations
- VirusTotal Integration: Paste a free API key for enhanced malware scanning.
- Cloud Security: AWS, Azure, and GCP monitoring for infrastructure changes.
-
Threat Intelligence — STIX 2.1 / TAXII 2.1
Connect any STIX 2.1 / TAXII 2.1 feed — your internal MISP instance, a commercial provider, or an open feed like AlienVault OTX — and nPro automatically ingests indicators of compromise and matches them against your live log traffic in real time. Configured entirely from the dashboard.
- Supports MISP, OTX, and any standards-compliant TAXII 2.1 server
- IOC matches surface as a flagged indicator directly in Offense Monitoring
- Air-gap compatible — matching engine runs locally, no outbound calls during detection
- Stays idle until you enable it — zero performance impact when not configured
- AI Analysis: Special AI button to analyze security logs and recommend solutions. Available on the Enterprise tier.
Architecture
Understanding nPro's Architecture
Four engines, one database, running entirely on your infrastructure.
XDR
Threat detection and response
SIEM
Log correlation and alerting
NRTG
Network monitoring
DLP
Data loss prevention
ClickHouse time-series database
One store for all four engines. Billions of events, sub-second queries, roughly 10:1 compression.
Your infrastructure
No outbound dependency. No vendor cloud.
Deployment modes
Single node
up to ~5,000 devices
Everything on one server. The simplest operational model and the right default for most deployments.
Distributed
higher event volume
Ingestion, processing and storage split across separate servers to handle larger estates.
Air-gapped
no outbound connectivity
Operates with no external communication at all, for classified and highly regulated networks.
Sizing
Optimised for Ubuntu 24.04 LTS. ClickHouse is columnar, so disk I/O is the primary bottleneck and SSDs are strongly preferred over spinning disks.
Retention and querying
Compression of roughly 10:1 on security log data makes long retention affordable on standard hardware. Query via the visual timeline explorer or direct SQL against ClickHouse.
Retention policies are set per log source, so high-frequency network flow data can age out faster than security events kept for compliance audits.
Log source compatibility
Ingests via Syslog over UDP or TCP, Filebeat, and direct API integrations. Custom parsers can be added through the pipeline configuration interface.
Getting help
Enterprise customers receive dedicated technical support with guaranteed response times. MSSP partners have a dedicated portal with deployment guides and priority escalation.